



This article discusses authentication choices. Current compatibility and recovery options depend on the deployed version and integration; historical examples do not establish a universal support or timing guarantee.
As organizations continue moving toward stronger authentication, many users are asking an increasingly important question:
"Do I really need an authenticator app, or can I simply use a hardware security key?"
The answer is:
Yes—and for many organizations, a hardware security key is actually one of the strongest forms of Multi-Factor Authentication (MFA) available.
FIDO2/WebAuthn security keys can provide phishing-resistant authentication when properly implemented. Evaluate the authentication protocol, configuration and recovery path rather than assuming that every mode of a physical key provides the same protection.
Even better, modern passwordless authentication platforms can integrate hardware security keys into a broader authentication strategy that emphasizes security, business continuity, and user productivity.
What Is Full Duplex Authentication® (FDA)?
The published FDA architecture describes an enrolled app checking its configured authentication-server relationship, with the person reviewing the expected request. Application authorization and session security remain separate controls.
Confirm recovery and backup procedures for the exact deployed version. Test device loss, replacement, revocation and unauthorized recovery before rollout; no universal recovery time is established here.
FIDO2/WebAuthn security keys can be evaluated as a separate authentication option. Compatibility with a particular PasswordFree or NoPass deployment requires version-specific integration evidence; naming a key vendor does not establish support.
What Is a Hardware Security Key?
A hardware security key is a small physical device used to verify your identity during authentication.
Instead of entering a one-time code from a mobile application, users simply:
Insert the key into a USB port
Tap an NFC-enabled security key against a mobile device
Connect via USB-C, Lightning, or other supported interfaces
Verify authentication with a touch or PIN, depending on configuration
The key securely proves the user's identity without requiring SMS messages or authenticator applications.
Popular examples include:
YubiKey®
Feitian security keys
Google Titan Security Key
Other FIDO2 and WebAuthn-compatible authenticators
Choose authentication methods against the application, account model and supported product version, then verify the integration in a controlled pilot.
Why Are Hardware Keys More Secure?
FIDO2/WebAuthn security keys use public-key cryptography with the relying party. Some mobile authenticators also implement cryptographic, phishing-resistant methods; the protocol and configuration matter more than whether the authenticator is a key or an app. WebAuthn
This provides several important security advantages.
Phishing Resistance
Traditional MFA often asks users to:
Enter passwords
Type one-time codes
Approve push notifications
Attackers can sometimes trick users into providing these credentials through sophisticated phishing websites.
Hardware security keys dramatically reduce this risk because the authentication process is cryptographically bound to the legitimate website or application.
Even if users accidentally visit a fake website, the key typically will not authenticate with the fraudulent site.
No Cellular Network Required
Unlike SMS authentication, hardware keys do not rely on:
Mobile carriers
Cellular service
Text messages
A key-based exchange that does not use SMS avoids these SMS-specific dependencies. Recovery or fallback paths may still reintroduce them:
SIM-swapping
SMS interception
Delayed text delivery
No Authenticator App Required
Many employees prefer not to install business authenticator applications on personal smartphones.
Hardware security keys eliminate that requirement entirely.
This makes them particularly attractive for organizations that:
Issue corporate laptops
Restrict personal phone usage
Operate in secure environments
Support employees without smartphones
Are Hardware Keys Better Than Authenticator Apps?
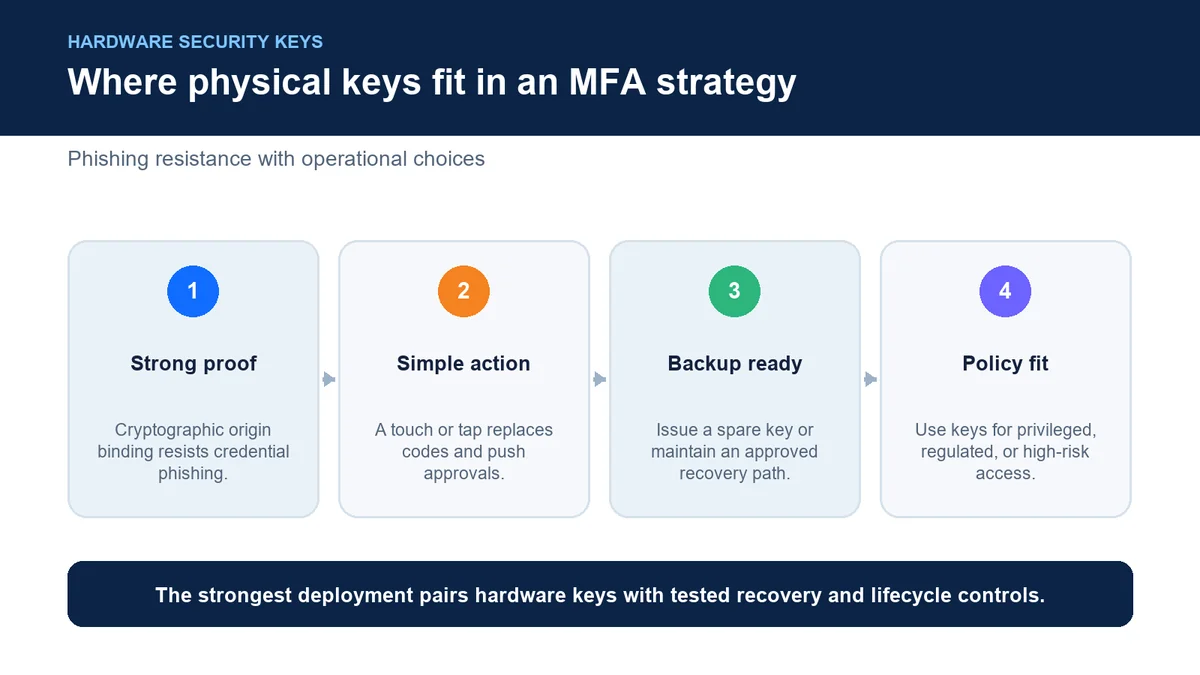
In many situations, yes.
However, every authentication method involves tradeoffs.
Authentication Method | Security | Convenience | Phishing Resistance |
SMS Codes | Moderate | High | Low |
Authenticator Apps | High | High | Moderate |
Hardware Security Keys | Very High | High | Excellent |
Passwordless Authentication Powered by FDA | Excellent | Excellent | Excellent |
Rather than viewing hardware keys and passwordless authentication as competing technologies, organizations increasingly use them together as part of a layered identity strategy.
Who Should Consider Hardware Security Keys?
Hardware keys are particularly valuable for:
System administrators
Executives
Financial institutions
Healthcare organizations
Government agencies
Developers
Privileged users
Organizations with Zero Trust security strategies
Many cybersecurity frameworks recommend phishing-resistant authentication for privileged accounts, making hardware security keys an attractive option.
The Challenge With Physical Tokens
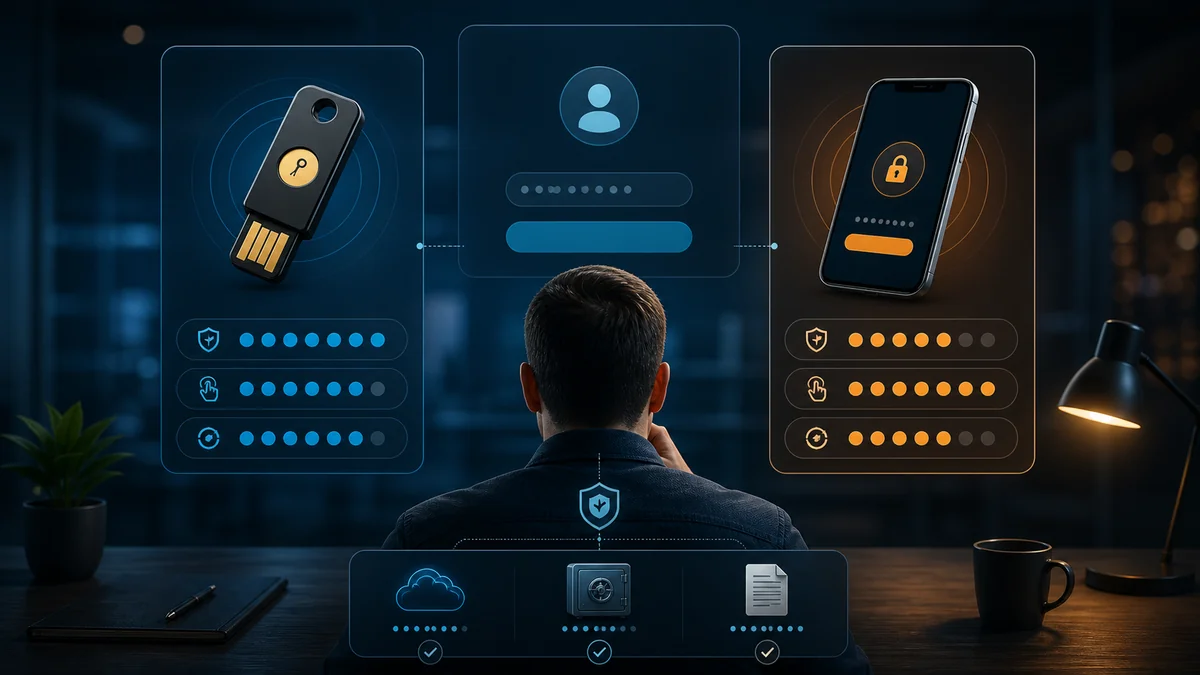
Like any physical device, hardware security keys can be:
Lost
Forgotten
Damaged
Left at home
Replaced
Traditional authentication platforms often struggle when this happens.
Modern authentication should anticipate these situations.
Built for Business Continuity—Not Just Strong Authentication
Security should never become a reason employees cannot work.
Authentication powered by Full Duplex Authentication® was designed around operational resilience.
Unexpected events happen.
Devices fail.
Hardware gets replaced.
Employees travel.
Authentication should continue working.
Emergency PIN Authentication
Evaluate any documented emergency-access method under the organization’s recovery policy; confirm availability, enrollment, expiry and audit behavior for the supported build.
This controlled recovery mechanism helps maintain productivity without compromising organizational security.
Secure Backup & Restore
Organizations using PasswordFree® or NoPass™ can enable Secure Backup & Restore, allowing authentication profiles to be securely backed up to:
Secure cloud storage
Corporate network infrastructure
When users receive a replacement phone or configure a new authentication device, they can restore their authentication profile.
Test restoration on an authorized replacement device and revocation of the previous device. Measure actual recovery time for the selected deployment.
Instead of rebuilding authentication from scratch, they simply resume working.
Choosing the Right Authentication Platform
Every organization has unique operational requirements.
PasswordFree® — Flexible SaaS Authentication
Organizations seeking rapid cloud deployment often choose PasswordFree®, Identité's Software-as-a-Service authentication platform.
PasswordFree® provides:
Passwordless authentication
Simplified administration
Reduced help desk workload
Secure Backup & Restore
Improved employee productivity
NoPass™ — Enterprise Authentication Without Compromise
Organizations requiring enterprise identity integration often choose NoPass™, powered by Full Duplex Authentication®.
NoPass™ supports:
Microsoft Active Directory
Microsoft Entra ID
Microsoft 365 / Office 365
Microsoft Azure
On-premises deployment
Customer-controlled cloud environments
Many banks, healthcare providers, government agencies, and other highly regulated organizations prefer NoPass™ because it combines deployment flexibility, enterprise identity integration, and phishing-resistant authentication while allowing them to maintain direct control over authentication infrastructure.
Best Practices for Using Hardware Security Keys
Organizations should:
Issue hardware security keys to privileged users.
Register backup authentication methods.
Configure Secure Backup & Restore for authentication profiles.
Train users on proper handling of security keys.
Replace lost or damaged keys promptly.
Hardware keys are strongest when they are part of a comprehensive authentication strategy.
The Identité Perspective
The question isn't simply:
"Can I use a hardware key instead of an authenticator app?"
The better question is:
"Which authentication method provides the strongest security while allowing my employees to remain productive?"
Hardware security keys represent one of the strongest authentication technologies available today, particularly for organizations seeking phishing-resistant identity verification.
But the most effective authentication strategy extends beyond any single device.
Evaluate passwordless methods, hardware-key compatibility and recovery as separate requirements. Obtain evidence for the selected product version, including failure and lost-device scenarios, before relying on them for business continuity.
Because modern authentication isn't about choosing between hardware keys and authenticator apps.
It's about building an authentication strategy that is secure, resilient, flexible, and designed to keep your business moving.