Who is participating?
Authenticate the enrolled account with the configured factors.
How it works / Full Duplex Authentication®
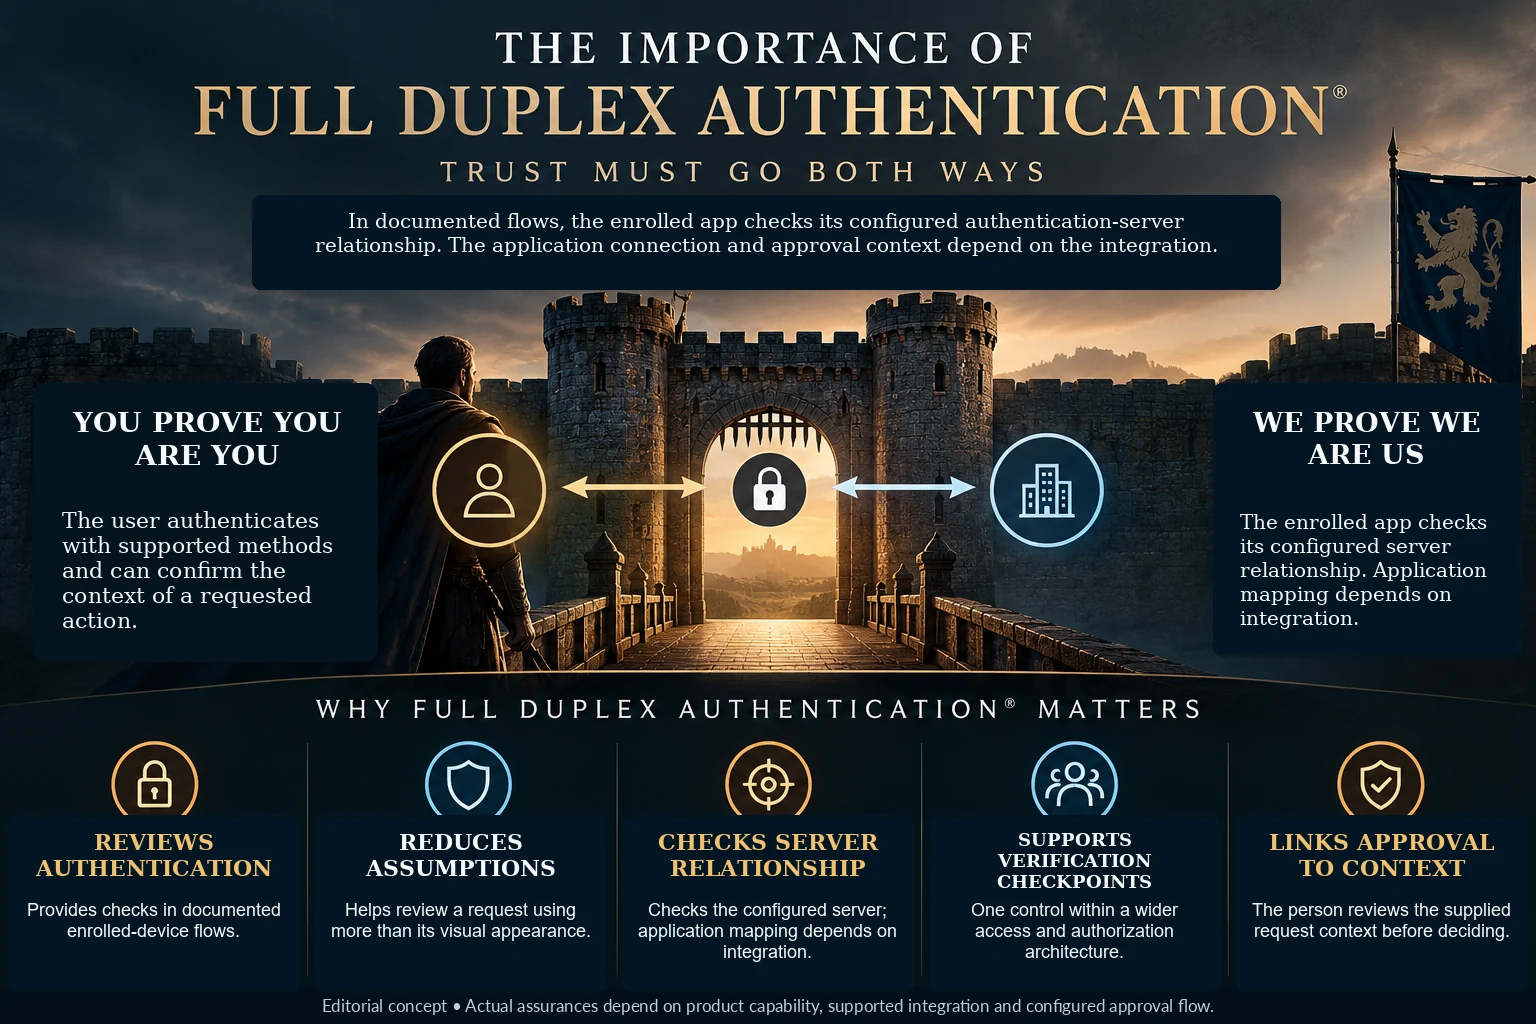
An organization needs to authenticate its user. The person also needs a reason to trust the service asking for approval. Full Duplex Authentication makes that relationship work in both directions.
 501501
Full Duplex Authentication connects account authentication, the enrolled app’s server relationship and a deliberate human decision. The comparison is the visible part of that experience.
Starts the request and owns account access or the pending operation.
Handles the configured authentication exchange.
Verifies its established authentication-server relationship.
Checks the request they initiated or expected, then chooses.
Authenticate the enrolled account with the configured factors.
The enrolled app checks its authentication server; the integration connects that server to the application.
A request can be expected without being initiated by the person, such as an agent-prepared action. The person still decides.
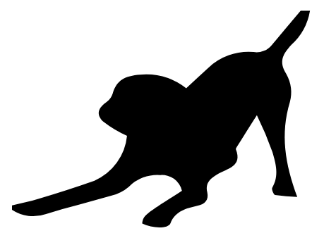
The customer sign-in example uses the documented BigCommerce LoginFree™ flow: scan the store’s QR code, compare the black picture and number on browser and phone, and accept in the browser. The customer reaches their account and the phone confirms success.
Try the authentication experience
Start with Sign in, then Scan, Compare and Result. Try the buttons, or use Tab and the arrow keys to explore.
Illustrative demo — no real sign-in or camera connection.
PasswordFree® · BigCommerce LoginFree · interactive example
An enrolled customer chooses PasswordFree to return to their account. Try the sign-in button in the store.
Your orders. Your account.
Open the enrolled app and point the phone at the store’s QR code. Here, select Scan QR code in the phone’s viewfinder.
Point your camera at the store
Compare the black picture and code on the two screens. If they match, select Accept in the store. If anything looks wrong, select Decline.
Do the picture and number match your phone?
501Compare with the store
501If they match, select Accept in the store. Otherwise, select Decline.
The store opens the customer account and the phone shows a green confirmation.
Try the highlighted button or use the controls below.
A person may be signed in while a particular operation still needs their approval. NoPass can request a fresh confirmation on the phone at that point. The application holds the operation and uses the response in its execution policy.
Authentication establishes the account relationship. Application permissions decide what that account may do; an operation-approval step asks for the person’s decision when it matters.
FDA authenticates an enrolled account in a configured service relationship. Initial identity proofing or KYC belongs to the organization’s separate process.
No. The enrolled app’s authentication-server relationship and the integration are distinct from the comparison presented to the person.
WebAuthn/FIDO2 supports phishing-resistant authentication through verifier-name binding. Start with an access or approval workflow you need to improve, and compare integration, user experience and recovery. FDA is not a replacement for every existing identity or authorization control.
 1 / 6
Strong passwords do not settle every security decision. Legitimate users can still be misled into approving the wrong request.
2 / 6Full Duplex Authentication® (FDA) brings mutual verification to digital interactions — authenticating the user and helping them verify the service and the intended action.
3 / 6Even strong users can be tricked into approving fraudulent requests. FDA helps reduce risk in supported flows:
Your Bank Review and approve this payment?
4 / 6FDA supports strong security and simpler access, for both customers and your workforce.
 5 / 6
From human users to AI-prepared actions, FDA helps organizations manage trust, access and approval in a rapidly changing digital world.
 6 / 6
Discover how Full Duplex Authentication® can help you reduce risk and enable secure, seamless experiences for your customers, your workforce and the AI-powered future.
Full Duplex Authentication is the shared foundation. Choose around the people and systems you serve.

Passwordless registration and sign-in for customer accounts, with integrations for supported stores and applications.
Explore customer access
Passwordless workforce access and approval checkpoints for sensitive actions in your applications.
Explore NoPassRead the patent, examine the published architecture and follow an implemented customer journey. A patent describes an invention; it is not a certification of a deployment.
A matching picture is not a reason to approve an unexpected action. Keep the account closed, decline the request and use the service’s known support route.
The service is waiting for the person’s decision.
Check the picture and number against the service you are using. A match alone does not grant permission.
This example shows a person choosing to decline; it does not simulate automatic attack detection.
Passwordless registration and sign-in for customer accounts, with integrations for supported stores and applications.
Explore customer accessPasswordless workforce access and approval checkpoints for sensitive actions in your applications.
Explore NoPassIdentité’s Full Duplex Authentication® connects a configured authentication-server relationship with an enrolled app and a deliberate human decision. The app verifies its established server relationship; the integration connects that server to the requesting application. The visible picture and number comparison helps the person review the request, and does not replace the underlying server checks. See the existing architecture and demonstration for the actual flow and product-specific limits.
It does not certify a deployment, perform KYC, remove application vulnerabilities, prevent every compromised-device attack or make all fraud impossible. Trusted enrollment, certificate and key management, endpoint security, revocation, recovery and meaningful context remain necessary. A patent describes an invention; it is not deployment certification.
How are passkeys different?Start with the published architecture, technical resources and an identified product version. Confirm trusted enrollment, the app-to-authentication-server relationship, the application mapping, key lifecycle, revocation and supported recovery with the integration owner.
A patent establishes an invention, not a deployment certification. An authentication result is not continuous authorization, a guarantee against session theft or evidence that every business field was cryptographically bound. The application retains permissions, session policy and execution controls.
For a later human decision, use the approval integration checklist. Ask which controls are documented product behavior and which the application must implement.
Evaluate authentication methods alongside enrollment, recovery, legacy dependencies and operational continuity. The seven-step enterprise guide connects architecture questions with a controlled migration plan.
Read the Enterprise Passwordless Migration GuideStart with the recovery process for your product and integration. Your organization should be able to revoke the old enrollment, restore access and review existing sessions. Confirm the recovery evidence and expected timing before rollout.
Enrollment connects an account with the supported app relationship. Identity proofing or KYC is a separate process when your service requires it; define who may enroll and how that person is validated.
Treat decline, expiry and an unavailable phone as distinct outcomes. Keep the operation on hold until application policy is satisfied, and give the person a clear route to retry or recover access. A delivered notification is not approval.
Keep the approval tied to the pending operation. Define which changed details require a fresh decision, how duplicate results are handled and how stale responses expire. Confirm the message and binding semantics with the integration owner.
The application owns permission and execution. Combine the approval checkpoint with the session controls, monitoring and policy reevaluation your organization needs.
Compliance depends on the complete deployment and the organization’s obligations. Assess enrollment, authenticators, recovery and operations against the applicable requirements; a product name or patent is not a certification.
Choose around the workflow you need. WebAuthn binds credentials to the relying party and origin; FDA adds its configured app/server relationship and human decision. Compare the actual deployment and recovery experience.
Use the current WordPress, BigCommerce or Shopify listing and setup guide to plan installation. Check the account model, multisite or multi-storefront needs, product version and recovery path with your integration team.
The enrolled user authenticates; the enrolled app checks its configured authentication-server relationship. The integration maps that relationship to the requesting application.
The person reviews the request; your application controls permissions and execution. That makes the checkpoint a practical part of your wider security architecture.