Help employees reach their work and keep sensitive decisions with the people responsible. NoPass™ brings mutual authentication and explicit operation approval to enterprise workflows.
An employee can be real while a request is misleading.
A familiar application asks for access. A message appears to come from an executive. A software agent prepares a consequential change. Verifying the employee is essential, and the employee also needs a basis for trusting what they are asked to approve.
FDA lets the enrolled app verify the authentication server and presents the comparison for the employee to check. This connects the authentication experience to the service and request, with an explicit human choice.
For example, an internal application can require approval before granting elevated access. It initiates NoPass confirmation and waits for the responsible person’s device response. An AI agent reaching a configured sensitive operation can use the same approval capability.
The application retains its permissions and execution rules. The owner decides which actions require this extra confirmation.
The application sends a NoPass approval request to the person responsible. Start the request in the application.
● ● ●Your work application
Example application request
Grant elevated access
NoPass
Enrolled deviceReady when you are.
The request reaches your phone.
Open the push notification on the enrolled phone. The application waits while you check the request.
● ● ●Your work application
Example application request
Grant elevated access
Waiting for your decision
NoPass
Approval requested
Grant elevated access
Check both screens. Then decide.
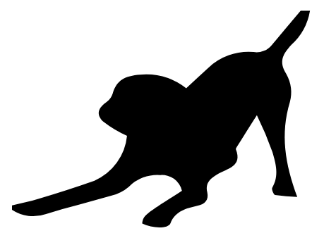
Compare the black picture and number. If this is the request you intended, select Confirm on the phone, using the local confirmation configured for your device, such as fingerprint or Face ID.
● ● ●Your work application
Example application request
Grant elevated access
Compare this picture and number with your phone.
501
Waiting for your decision
NoPass
Do you approve this access request?
501
Approved — back to application policy.
Approval received. The application still applies its own permissions and execution policy before carrying out the operation.
● ● ●Your work application
Example application request
Grant elevated access
Approved
NoPass
Confirmed
Your approval has been sent.
Try the highlighted button or use the controls below.
Central administration gives the IT team a place to manage users, devices and authentication activity. Federation, RADIUS and Desktop Unlock provide routes for the access points people already use.