


Skip to content
IdentitéTrust starts here
English
EnglishEspañolPortuguês
Contact

Integrations

Add mutual trust where your systems meet people.

Connect a customer account, an employee access point or a sensitive-operation checkpoint. Keep the application’s business logic and bring Identité® authentication to the interaction that needs it.

An engineer testing a mobile application in a development team
Your application. A trusted experience.

Trace the request across the system.

Full Duplex Authentication® sits behind the supported app-based experience. Map the application, configured authentication service and enrolled device before deciding where the person confirms the request.

The application owns the final access decision.

  1. Application or gateway

    Starts the request and owns the account, session and permissions.

  2. Configured integration

    A commerce plugin, SDK, federation provider, RADIUS adapter or Windows component.

  3. NoPass™ authentication service

    Coordinates the supported authentication flow with the enrolled app.

  4. Enrolled device

    Verifies the authentication service and supplies the configured user confirmation.
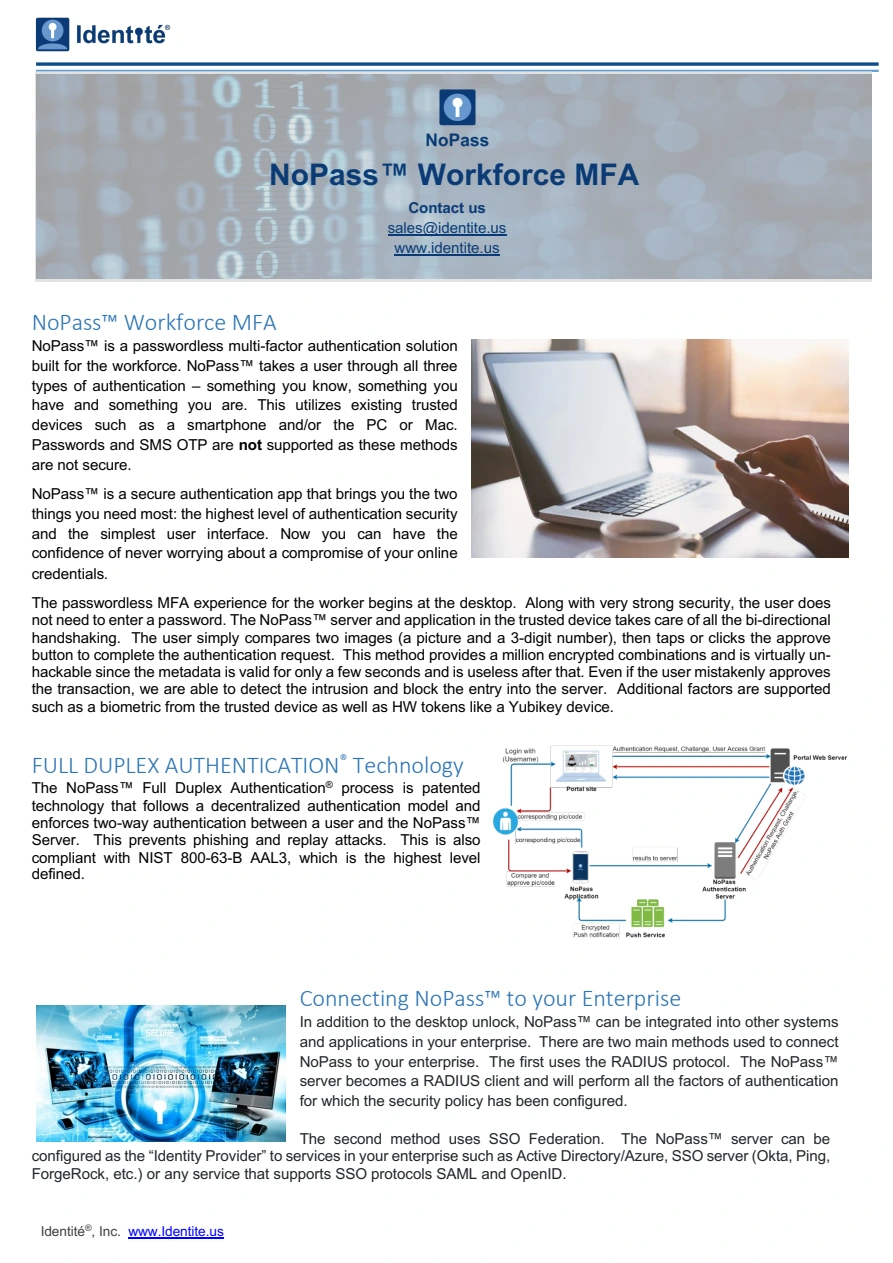
A federated application is a concrete starting point.

For a configured SAML or OpenID Connect integration, NoPass acts as the identity provider. The relying application requests authentication, NoPass handles the enrolled-device exchange, and the application uses the result to apply its access policy.

The application keeps its business functions and permissions. The account source and user mapping connect the existing identities to the chosen configuration.

Choose the interaction you need to connect.

Choose the interaction you need to connect.
InteractionRoute or componentResponsibilityGuide or next step
Customer registration and returnSupported platform pluginMerchant / developer: platform configuration and customer accounts.Choose a customer platform
Business application sign-inConfigured SAML / OpenID Connect federationIdentity provider and service provider: mapping and authentication; application: access policy.NoPass federation guide
Network or remote accessThe gateway’s configured RADIUS pathGateway and RADIUS integration owner: target configuration.NoPass technical documentation
Windows login and unlockNoPass Windows components and enrolled phoneIT / support: workstation setup and device lifecycle.Desktop Unlock planning and example
Custom applicationSupported SDK / proxy pathApplication team: client integration and result handling.SDK integration planning
Sensitive operationApplication-initiated NoPass approvalApplication owner: pending operation, permissions and execution policy.Operation-approval planning

Working in a Microsoft environment.

For Windows workstation access, start with Desktop Unlock. For a directory-backed business application, connect its account mapping and the applicable federation configuration. These are distinct access points, with their own setup guidance.

The integration team can identify the supported configuration for your Windows, directory or federation environment.

The details that make an integration work.

For your selected route, agree account mapping, enrollment and recovery, result handling and operational ownership. Those are the shared implementation questions; each platform guide supplies its specific setup steps.

Start at an explicit federation boundary.

The documented NoPass federation configuration connects an identity provider and service provider. A supplied Keycloak integration uses a NoPass authentication step before Keycloak completes its configured protocol flow. The target application still controls the resulting session.