What is mutual authentication?
Mutual authentication is an exchange in which each party verifies the other. In a digital service, authenticating an account to a server and authenticating the server to a client are distinct checks. The evidence, the trusted identities and the protocol determine what has actually been established.
Two directions, not a count of factors
A password can prove possession of a secret to a service without proving which service is asking for it. MFA combines distinct factor types in authenticating an account. Mutual authentication describes the directions of verification. A system can use both; adding another factor alone does not establish every part of the service relationship.
What is destination verification?
Destination verification checks that the endpoint asking for authentication belongs to the intended service relationship. It involves a trusted reference, such as a certificate name or an enrolled server, rather than a familiar-looking logo. The browser origin, authentication server and business application may be different components: the integration must connect them correctly.
What do TLS and mTLS establish?
In ordinary TLS, the client validates the server certificate against its trust policy and the intended name. TLS protects the channel; a valid certificate is not a promise that its owner is honest. TLS can also request a client certificate. Mutual TLS (mTLS) authenticates both channel endpoints using certificates. A client certificate may represent a workload or device; it does not automatically prove a person’s legal identity or consent to a particular transaction.
How are passkeys different?
WebAuthn credentials are scoped to a relying party (RP ID). The browser constrains their use and the relying party validates the origin and RP ID hash in the authentication response. This verifier-name binding resists credential use on a phishing origin. Passkeys therefore do not ignore the domain. Yet successful account authentication, a person understanding an operation and an application authorizing it remain distinct decisions. Recovery and fallback paths also belong in the evaluation.
Where does intent fit?
An expected request is not necessarily one the person initiated: an application or AI agent may prepare an action. Before approval, the person needs enough context to decide whether the request is expected and acceptable. The application must separately enforce permissions, scope and execution policy. Approval cannot grant an agent permissions it does not have.
How does Full Duplex Authentication fit?
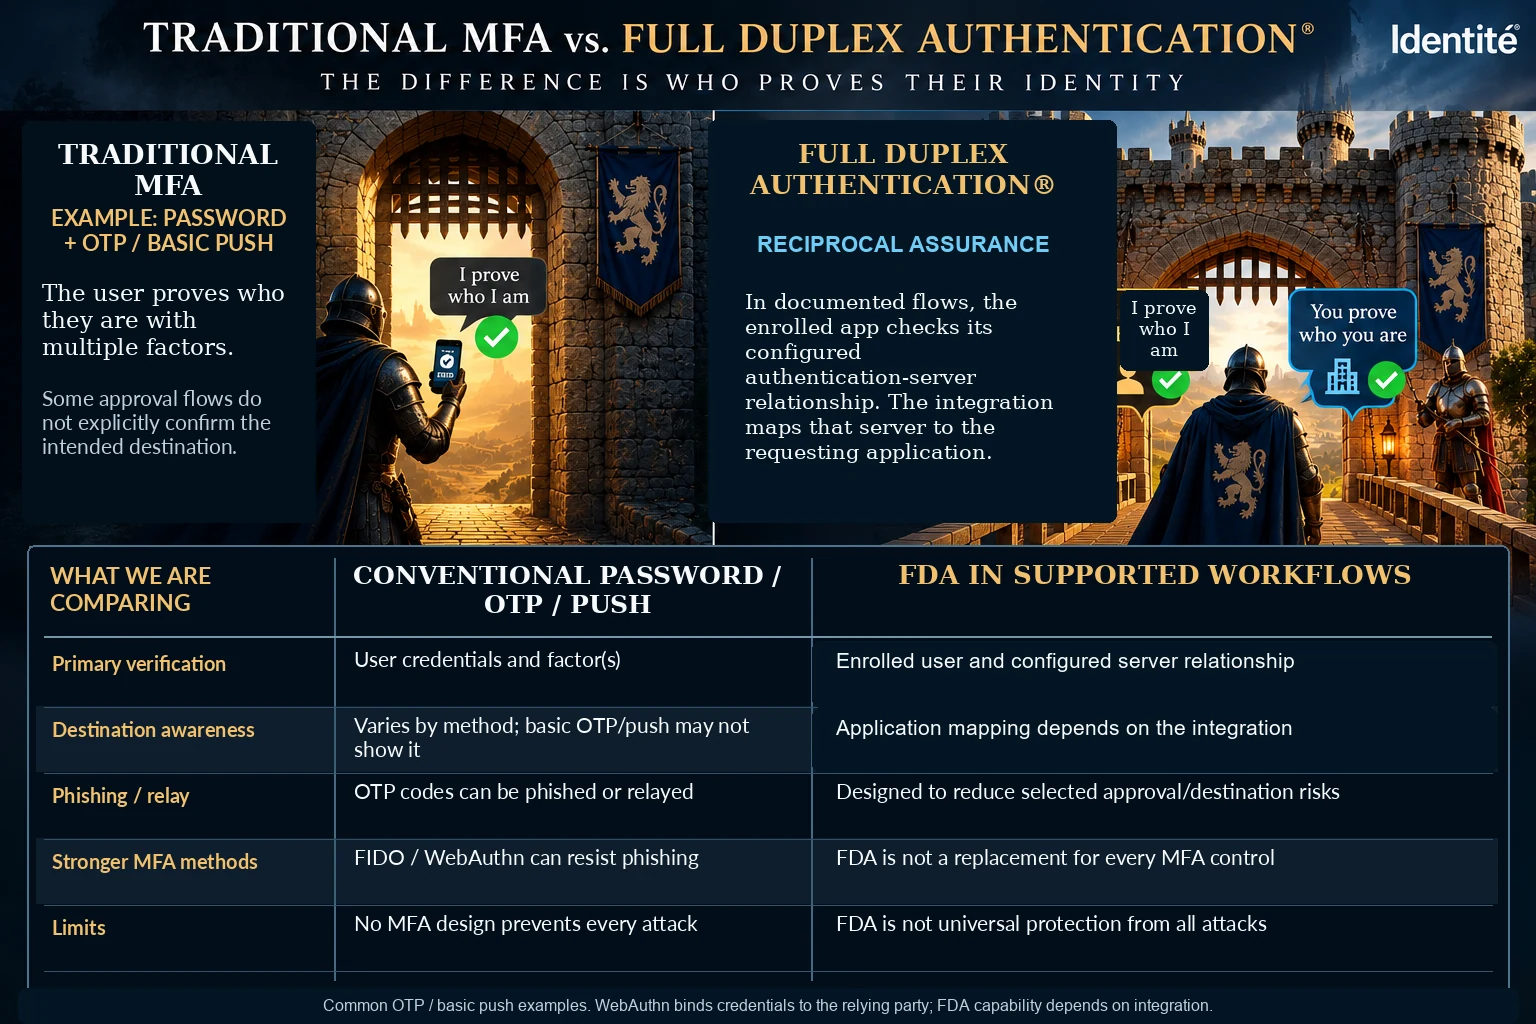
Identité’s Full Duplex Authentication® connects a configured authentication-server relationship with an enrolled app and a deliberate human decision. The app verifies its established server relationship; the integration connects that server to the requesting application. The visible picture and number comparison helps the person review the request, and does not replace the underlying server checks. See the existing architecture and demonstration for the actual flow and product-specific limits.
Where can these checks help?
For customer sign-in, check the service and the request before opening the account. For workforce access, evaluate enrollment, device protection and recovery alongside authentication. For a sensitive operation or agent-prepared action, keep execution pending until the application’s authorization policy and the required human decision are satisfied. These are different workflows, with different integration requirements.
What does mutual authentication not solve?
It does not certify a deployment, perform KYC, remove application vulnerabilities, prevent every compromised-device attack or make all fraud impossible. Trusted enrollment, certificate and key management, endpoint security, revocation, recovery and meaningful context remain necessary. A patent describes an invention; it is not deployment certification.
What is verifiable identity, and how does it relate to digital trust?
In Identité’s approach, verifiable identity means a relationship supported by evidence about who is participating, the connected destination and the request being considered. Digital trust also depends on what that relationship allows: permissions, accountability and a person’s decision. Account authentication does not by itself prove legal identity or authorize every subsequent action.