

Updated NIST Guidelines for Authentication
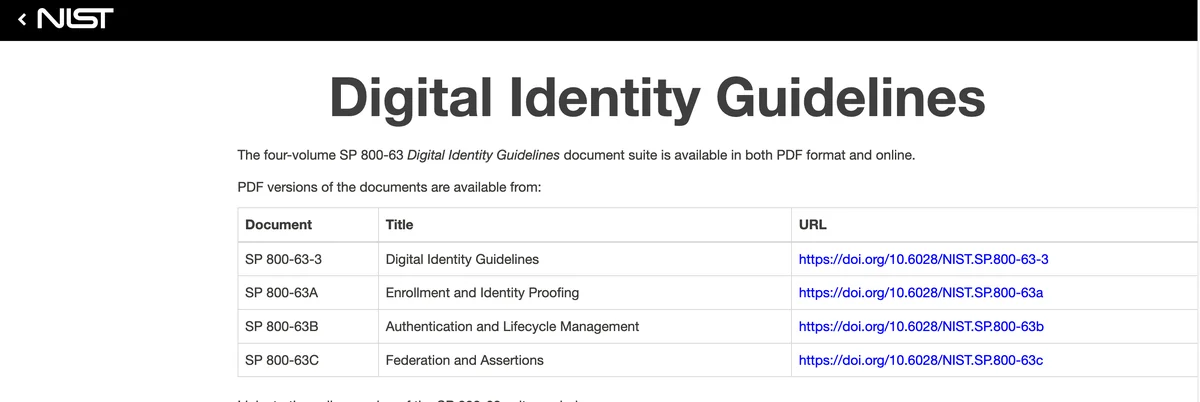
NIST released a fully updated version of the publication 800-63-B in June 2017. This further defined the different levels of authentication in terms of strength. A revision in March 2020 added a better explanation for “verifier impersonation resistance”. This is a key defense against all forms of social engineering, MitM, Browser-n-Browser, website impersonation, and Phishing attacks.
How strong is your authentication?
NIST defines three authentication assurance levels. AAL1 permits single-factor authentication, with MFA recommended as an option; an application selects its assurance level through a risk assessment. A password plus an approved possession authenticator can use two distinct factors. Typing an OTP does not turn it into a knowledge factor, although an attacker can relay that code through a fake login page. NIST 800-63-B publication
AAL2 requires two distinct factors and at least one replay-resistant authenticator. Under SP 800-63B-4, applications at AAL2 must also offer a phishing-resistant option. Email is not permitted for out-of-band authentication; SMS over the public telephone network is restricted and requires additional checks. SMS should therefore not be dismissed as merely a second password, nor treated as equivalent to phishing-resistant authentication.
AAL3 requires two distinct factors and phishing-resistant public-key authentication with a non-exportable authentication key. Recognizing a fake website is useful, but user awareness alone cannot provide these protocol protections. Verifier impersonation resistance must be established by the authenticator and its deployment, not by expecting the person to detect every deception.
Authentication should be simple and secure
There is no debate on why authentication needs to be simple. Authentication is the number one source of friction for new and returning users to a website application. We are now seeing website and application registration techniques that eliminate passwords by simply clicking on a social icon. Returning users are not prompted for a login, which makes it very convenient for the authenticating user.
This is usually done via a common protocol called OAuth, which dispenses a digital token that essentially allows for the authorization of certain actions without requiring full authentication. Unfortunately, users are still authenticated with at least a traditional username and password before the token can be granted. These social service login dialogues are easily impersonated. Thus, users can still be easily tricked into authorizing a token for the bad actor as well.
Passkeys using WebAuthn bind credentials to the relying party and validated origin, resisting their use on an unrelated phishing site. They do not establish the trustworthiness of a business or authorize every subsequent action. AAL3 is not a universal requirement for every website: the appropriate level depends on risk, and a particular passkey deployment must be assessed against that level’s requirements.
This does not mean that a user needs to perform additional steps to ensure higher levels of security. In fact, the more actions made by a human that we can replace with technology during the authentication process, the more secure authentication becomes. This is because, as the saying goes, “we are only human”.
Full Duplex Authentication®
Identité’s Full Duplex Authentication® introduces service authentication before the person’s approval through the enrolled app. That design goal is relevant to verifier impersonation resistance, but a patent or product description is not an AAL3 assessment. A deployment must separately demonstrate the required key protection, distinct factors, cryptographic properties and lifecycle controls.
Summary
At Identite®, we have integrated Full Duplex Authentication® and other factors such as biometrics and hardware tokens into our solutions for both the workforce and online customers. We offer both of our PasswordFree Authentication® solutions via a Platform as a Service (on-premise) as well as via Software as a Service for online customers.
To learn more about how Full Duplex Authentication® can greatly improve the user experience for online customers during authentication and offer the highest level of protection for users against phishing, please visit us at www.passwordfree.us. More information about our PaaS offerings can be found at www.identite.us. For more details about the NIST update https://pages.nist.gov/800-63-3/
Blog Post by Joe Skocich @Identite.us