




What is CAPTCHA?
CAPTCHA stands for Completely Automated Public Turing Test to Tell Computers and Humans Apart. It evaluates whether an interaction appears human; it is not the same as authenticating an account. Its effectiveness and accessibility depend on the technique and deployment, and automated attacks can defeat some challenges.
What are the pros and cons of CAPTCHA?
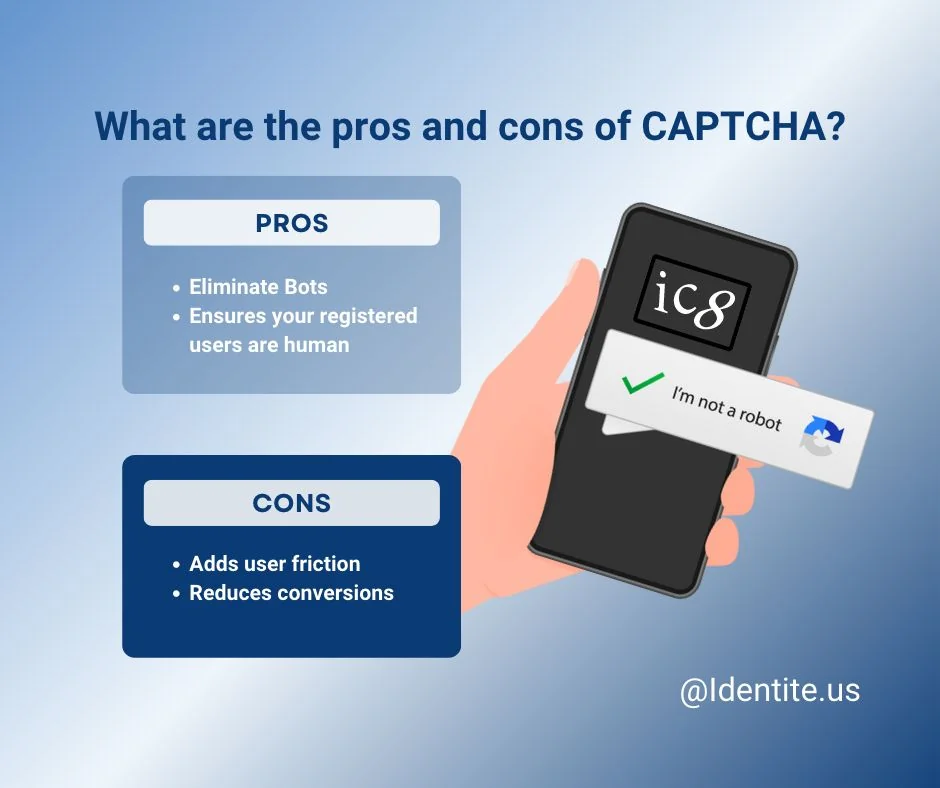
The pros and cons seem to weigh differently, depending on who you are asking and what issue is being addressed. The Chief Risk Officer might be trying to address the issue of “fake accounts” or “spam” registrations. If this leads to fewer conversions, the risk outweighs the reward.
What is PasswordFree® MFA and how does it also make your site bot resistant?
PasswordFree® uses an enrolled-device workflow and Full Duplex Authentication® to support configured account authentication and service verification. Supported local confirmation and biometric activation depend on the device and deployment. A human decision in this workflow is not proof that every request is free of automation or abuse; enrollment, endpoint security and recovery remain necessary.
Do I need both CAPTCHA and PasswordFree® MFA?
Whether CAPTCHA is still needed depends on the workflow and abuse being addressed. Account authentication and a device approval can reduce reliance on some interactive challenges, but do not replace every bot, scraping or registration-abuse control. Evaluate completion and accessibility with representative users, and retain separate rate limits and abuse detection where needed.
Conclusion
CAPTCHA in its conspicuous form has certainly outlived its original purpose. What seemed to make things worse was that CAPTCHA programs would purposely take users through a second round randomly even if the first round was a pass. By taking users through a second round of CAPTCHA, it was thought that this too would make it difficult for bots as most were designed to get through a single round. By moving to an inconspicuous approach where a user doesn’t even know CAPTCHA is there, there may still be a good case as long as it's not slowing down the website's performance.
Consider replacing a CAPTCHA challenge only when the proposed account and device workflow addresses the same concrete risk. Measure usability, accessibility and residual abuse rather than assuming universal bot or phishing protection from authentication alone.
Visit us at: https://www.identite.us/passwordfree-mfa to learn more.