
Passwords rely on a shared secret, while authentication mechanisms using public-key cryptography do not give the verifier the same private secret as the user. Reused or disclosed passwords remain vulnerable to phishing and credential stuffing. The relevant distinction is how a credential is protected and bound to its intended verifier, rather than whether every MFA solution shares a secret.
The end user has the responsibility for safeguarding credentials despite how perceptive and careful they are. This transfer of authentication challenges is one way from the user to the service, website or network. This opens the door to Man-in-the-Middle, Man-in-the-Browser, phishing and imposter websites that are springing up at a phenomenal rate.
Recent examples of this weakness are the hacks by passwordless vendors Microsoft and Okta, (BankInfoSecurity, March 22, 2022). While passwordless and Multi-Factor Authentication (MFA) are worthwhile goals, the one-way transfer that current methods use make them fall short in providing organizations adequate security while simultaneously delivering a simple and reliable user experience.
Once breached, your organization must navigate the series of disclosures for PR purposes or government mandates. These can create serious impacts on you and your organization including:
31% of consumers surveyed say they discontinued their relationship with the company that had a data breach
Of those consumers affected by one or more breaches, 65% say they lost trust in the breached organization
Stock Prices Drop an Average of 5 Percent when the Data Breach is Disclosed
Because the credential transfer is one-way, a hacker can easily install themselves between the user and the service to intercept anything the user is sending to the service and then replicate it later to gain access. This has happened too many times to continue accepting the risk of one-way authentication.
Full Duplex Authentication® adds a service-authentication step before the person approves the request through an enrolled app. This is intended to reduce impersonation risk in the configured authentication relationship. It does not make man-in-the-middle, browser compromise or phishing risks universally disappear; protection depends on the protocol, integration and security of the participating devices.
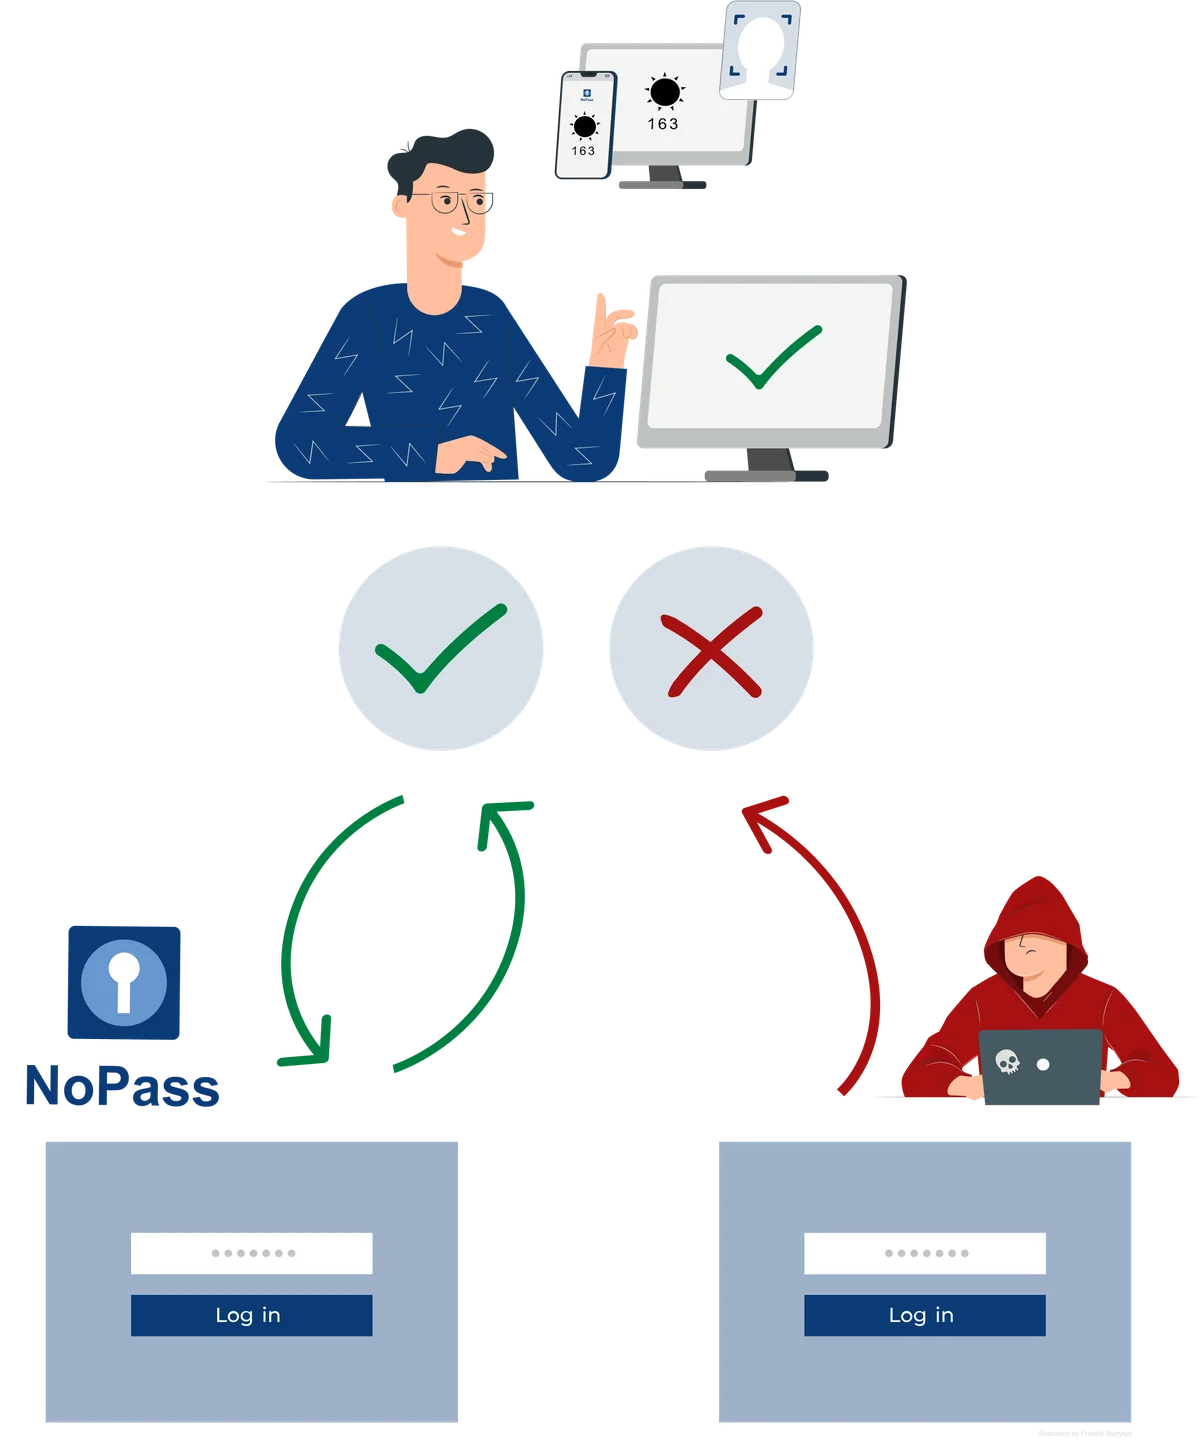
In the illustrated login flow, the person checks the picture/number combination and approves or declines the request. An unexpected request should be declined because it was not initiated by that person. Removing the password reduces password-theft opportunities, but the decision still requires an enrolled device, a correctly connected service and attention to the request context.
The Full Duplex Authentication® model delivers some key benefits:
Users know they are on a valid website or network. The peace of mind this brings allows them to transact more comfortably and more often knowing they aren’t being compromised by imposter websites
Authentication is more natural which creates a more pleasant user experience. Happy users become long-term clients allowing you to gain market share from other vendors that don’t employ Full Duplex Authentication® as part of their security suite
No user data is sent until the server is authenticated
Multi-Factor, Multi-Channel user verification
Avoids exposing a manually entered SMS OTP in the illustrated approval flow; metadata transmission alone does not prove that every session or token is immune to interception.
Keeping biometric verification on the device can reduce exposure of centrally stored biometric data. Account records, recovery information and other personal data still require their own protection and retention controls.
Eliminating the password removes password reuse and password-theft paths from that login flow; authorization, recovery, endpoint protection and session security remain separate responsibilities.
Audits are much easier since you no longer have to worry about how your company protects, grants access to, encrypts and manages passwords
Full Duplex Authentication® is Simple and Secure
The adoption of modern multi-factor authentication technologies is one of the most impactful steps that can meaningfully reduce a company’s risk to compromised identities. More organizations are investigating and planning to move to passwordless technologies that include technologies like biometrics and public key cryptography in widely accessible devices.
The Full Duplex Authentication® process improves security with the two-way authentication for encrypted tokens and biometrics all while reducing friction from a truly passwordless process. From financial services to the healthcare sector, large enterprises are adopting passwordless systems at a remarkable pace and are seeking to transition to a more secure architecture. NoPass™ enhanced security finally protects both enterprise and the user leading to far greater levels of trust.